

Share


Aug 27, 2026 - 15 min read
Announcements
August 22 Exploit Post-Mortem
On Friday 21 August 2026 at 23:41 UTC, an attacker exploited a vulnerability in the contracts associated with the bridge configuration on Base and BNB Smart Chain (BSC), enabling the attacker to mint unbacked SAND without a corresponding deposit on Ethereum.
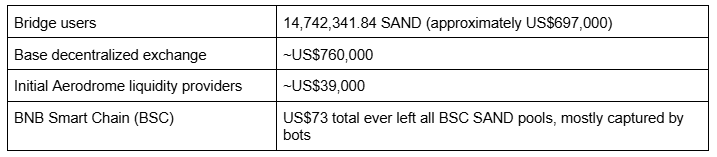
Over the next few hours, the attacker sold part of the unbacked SAND on Base and used another part to initiate redemptions from the collateral held in the Ethereum vault contract. Based on our current forensic analysis, this resulted in the withdrawal of 14,742,341.84 SAND, with an estimated value of approximately US$697,000.
The bridge was closed at contract level on all three chains on 22 August 2026, 05:26 UTC by The Sandbox team, and no SAND has been withdrawn since 22 August 2026, 02:21 UTC. This exploit did not apply to SAND on Ethereum or on Polygon. Ethereum SAND was not affected and the total Ethereum SAND supply remains unchanged at 3,000,000,000 tokens. SAND on Polygon uses a separate bridge that was not part of the affected path and has no identified exposure to the compromised contracts. Balances on both chains are intact and no user action is required.
Every wallet that held legitimately bridged SAND on Base or BNB Smart Chain immediately prior to the incident will be compensated 1:1 in SAND on Ethereum. The claim process will open within the next two weeks and will remain open for two weeks thereafter.
How the exploit worked
The bridge allows SAND to move between Ethereum, Base and BNB Smart Chain, and it works like a bonded warehouse. To send SAND from Ethereum to Base, a user deposits SAND into a vault contract on Ethereum, and the corresponding amount of SAND is then issued on Base.
To bridge back to Ethereum, the Base SAND is burned, and the Ethereum vault releases the corresponding amount of SAND against a signed delivery note confirming the burn and authorizing the release.
The exploit happened in the SAND token contract on Base and BNB Smart Chain. Those contracts carried a convenience feature that enabled anyone to ask the token to make a call on their behalf, which was intended to save users a transaction. As the token contract also served as the bridge's registered application on those chains, the bridge's messaging layer treated instructions originating from the token as instructions from The Sandbox.
The attacker made four moves:
- Obtaining administrative access. The attacker used the vulnerable call mechanism to cause the token contract to submit a request to register the attacker-controlled address as the authorized administrator. The bridge accepted the request because it originated from the registered token contract.
- Altering verification settings. With administrator rights, the attacker changed the verification configuration for incoming bridge messages so that the attacker-controlled address became the sole verifier and a single verification was sufficient for transaction confirmation.
- Minting unbacked SAND. The attacker submitted bridge messages representing deposits that had not occurred on Ethereum. The messages were verified under the altered configuration, and the relevant contract issued SAND on Base and BNB Smart Chain without corresponding deposits.
- Redeeming and realising value. The attacker realised value in two ways. First, the attacker sold unbacked Base SAND on Base exchanges for real ETH. Second, the attacker used some of the unbacked SAND to initiate reverse-bridge transactions. The unbacked SAND was burned, and the Ethereum vault released SAND against messages that were processed under the compromised verification configuration.
The sizing shows how deliberate this was. Thirty-nine blocks after the first mint of unbacked SAND, the attacker minted 14,743,364.21 SAND, exactly 100 SAND less than the 14,743,464.21 the vault held at the time. The attacker then bridged it to Ethereum and drew the vault down in six withdrawals, the last of which was sized to leave precisely 100 SAND behind.
The attacker did not receive all of the amount originally minted for redemption. Forty-eight minutes before the attacker’s own messages cleared, an unrelated arbitrage bot had already redeemed 642,471.52 unbacked SAND that it had bought on the open market, and two smaller withdrawals took a further 5,409.03 unbacked SAND. The attacker therefore received 14,095,483.66 SAND rather than the full amount targeted for withdrawal, falling short by 647,880.55 SAND.
Nothing about the return trip was forged. The burns were real, the messages were verified by the normal validators, and LayerZero's own delivery service carried them. The vault simply had no way to confirm whether the Base SAND being burned had ever been backed by a deposit, which is why a third party could redeem the unbacked SAND just as easily as the attacker could.
Note: No keys held by The Sandbox were compromised, lost, or used by unauthorized parties at any point.
No new privileged account was granted. In particular, no super-operator was added on either affected chain, which we have verified against the attacker address, both attacker-controlled delegate contracts, the token contract itself, and the governance multi-signature wallets.
The LayerZero delegate roles on Base and BNB Smart Chain were taken by the attacker. No other privileged roles on any chain were affected. The delegate was not taken by obtaining a key; it was reassigned by the token contract itself, acting on the attacker's instruction.
Detailed Events Timeline
2026-08-21, 21:23:49
Attacker funds the operating wallet 0x67624bfadee937c9281b4f98ce18af1bee01257e on
Base with 0.015 ether, 2 hours and 18 minutes before the attack begins.
https://basescan.org/tx/0x09e6b57678cfa7719dfefcf0c3e38266bc7469841153f7dfb111779b4ec43990
2026-08-21, 23:41:41 Base, block 50,283,177
The LayerZero delegate role is hijacked.
https://basescan.org/tx/0x149eb0eec5f1c793b094b46889059b510281a7eff3c1597bb262777a5cfaa237
2026-08-21, 23:42:05 Base, block 50,283,189
First unauthorised mint, 50,000,000 SAND.
https://basescan.org/tx/0xbddb102a5dbc9324a84390aaa5a9767b89c2bac8955d486fe1cf697e2e9a8fa9
2026-08-21, 23:42:09 Base, block 50,283,191
First sale of unauthorised SAND.
https://basescan.org/tx/0xf4ea3fb662c23aec4155db32f2c3fdddcebd07adcbc5cb782a8b0388618a7d4b
2026-08-21, 23:42:18 BNB Smart Chain, block 117,321,966
The LayerZero delegate role is hijacked, 37 seconds after Base, using byte-for-byte identical transaction data.
https://bscscan.com/tx/0x7ca710d5f575276e12ed7a3617a65002159c87d512fb19e6f59bc31b46b19c95
2026-08-21, 23:42:45 BNB Smart Chain, block 117,322,026
First unauthorised mint, 50,000,000 SAND.
2026-08-22, 00:32:11 Ethereum, blocks 25,806,879 to 25,807,341
Collateral is released from the adapter in ten transactions totalling 14,742,341.841492 SAND, of which 14,095,483.660582 SAND went to the attacker's Ethereum wallet in six transactions and 646,858.180910 SAND to a third-party arbitrage bot in four transactions.
https://etherscan.io/tx/0x468d7438c58cb28df28f48a548ca479fc56f1493903024d42d5f744409a6f338
https://etherscan.io/tx/0x3617940c8a28978a23a717e93305298a6decdee4cf66aa02d7428118012ab7f0
https://etherscan.io/tx/0x2fbde0f46a34d081b3962dbb434cc293156ff9d8e8d5cb742664ed8dd5793ae3
https://etherscan.io/tx/0x6abe08955b1d8cc63cdebe0710eff2889bb8e71588cfd1c1c2347100a437f6ef
https://etherscan.io/tx/0xa3ec04aeb988b99f55096ef5cb199441f68d21bde75264c7eb84c66c4022076e
https://etherscan.io/tx/0xb4a661df02b1c6c7655cf3ef4adc454c1cfdd067c7ca8f4ee725c8b89a3b89fc
2026-08-22 00:35:23
Attacker sells 12,685,935 SAND on Ethereum mainnet for WETH 58.35
https://etherscan.io/tx/0x50c53e30372cf15cd38fed933d72a404c3860e410b9b2750577cae134ee60504
2026-08-22 00:58:11
Attacker sells 1,409,548 SAND on Ethereum mainnet for WETH 19.89
https://etherscan.io/tx/0xb9c67af6d87112c21a90505692d99f8c8944fcc681f7c536aa7714d0199fd90e
2026-08-22, 02:21:27 Base, block 50,287,970
The attacker's final sale. No further value is extracted after this point on any chain.
https://basescan.org/tx/0x4421af9af8685cb8ef76019beede442ab660e885b28ef8552f643c559b93ecda
2026-08-22, 03:15
ANOMALY DETECTED. The Sandbox and Animoca Brands senior executives are made aware of the incident and immediately activate the appropriate procedures involving the respective operational teams across the globe to address the issue.
2026-08-22, 03:31:23 Ethereum, block 25,808,009
The attacker's final transaction.
https://etherscan.io/tx/0xa53fef65f250f7d1a6fcf8001fd4cfecf75d3210b42d931084f087ecd1489c1a
2026-08-22, 03:35
Emergency action group is formed, comprising all senior Tech (based in EU) and Finance team (based in ARG) members under the oversight of the management team.
Initial diagnosis and scope of the incident are assessed and an investigation into the cause of the exploit is launched. Simultaneously, the team begins preparing external communications to security groups, exchanges and the public.
Containment transactions start to be prepared to pause bridging to Base and BNB in order to prevent further funds being deposited into the bridge and transferred to ETH mainnet.
2026-08-22, 03:40:01
The emergency containment transaction batch is prepared.
2026-08-22, 04:52:23 BNB Smart Chain, block 117,363,297
The attacker's final delegate change.
https://bscscan.com/tx/0x4bc85ff5c30e425e0a509a9ca19d5a13110fc6928d8f322f7c6ba08d4c72d3d8
2026-08-22, 05:09:19 Base, block 50,293,006
BASE CONTAINED.
Both peer routes are set to zero and the send function is disabled, in a single atomic transaction.
https://basescan.org/tx/0x3efb7d45facdab235ae349eb9461a5899c79b8ec6084dc58412a6f47c3fbd64b
2026-08-22, 05:16:29 BNB Smart Chain, block 117,366,511
BNB SMART CHAIN CONTAINED.
https://bscscan.com/tx/0xe2bc6f13c7778004561c1629161ad9f7521a86f0e49171d629ce78beeb04edbb
2026-08-22, 05:25:59 Ethereum, block 25,808,579
ETHEREUM CONTAINED.
https://etherscan.io/tx/0x20766750f80e037302626cfb813958136cd4eabf98100df0432c7521323c0bfd
2026-08-22, 07:22:00
Official communication released using The Sandbox official X account: https://x.com/thesandboxgame/status/2091063415649251821?s=46
What was the impact
The overall estimated economic impact was approximately US$1,496,784, calculated on the basis set out below. Of this amount, the attacker successfully captured US$987,000 through two key routes:
- Selling the unbacked SAND on Base
93,415,334.861816 SAND across 26 sales, all into a single pool: Aerodrome Slipstream SAND/WETH at 0xa69cdf524d072c366fd050957880552916d29405. Proceeds 327.592005773324842721 wrapped ether.
The pool held only 16.272817 wrapped ether when the attack began, so the attacker extracted more than twenty times its entire depth. This was possible because they programmed each sale as an exact-output swap requesting roughly 90% of the available ether the pool held at each instant, then waited for arbitrage bots to buy the crashed token and replenish the ether side. The attacker repeated this 21 consecutive times, pushing 313.32 wrapped ether back in from 79 trading contracts run by 534 separate accounts.
The final sales show the mechanism breaking down when the bots stopped buying: the 22nd attempt returned 86.8% of the pool, followed by 83% and 67.6%, with the last two putting 30.5 million SAND in for 0.000036 wrapped ether between them.
- Redeeming unbacked SAND at par
The attacker minted unbacked SAND on Base and invoked the reverse-bridge function to send SAND from Base to Ethereum. Three independent checks confirm the Ethereum side was honest, not compromised:
- The drain transactions were submitted to LayerZero's Executor 0x173272739Bd7Aa6e4e214714048a9fE699453059 by an executor operator, not by the attacker.
- The adapter's receive library is still the explicitly pinned 0xc02Ab410f0734EFa3F14628780e6e695156024C2
- The adapter's LayerZero delegate is still the Sandbox Safe.
A lock-and-release vault cannot distinguish a burn of legitimate tokens from a burn of unbacked tokens.
All three contracts are direct deployments with no proxy, so both arbitrary-call functions are immutable in bytecode. And because EndpointV2 permanently authorises the OApp to configure itself, delegate control over the Base and BNB Smart Chain contracts is contestable forever. Any reclaim can be undone by anyone for the price of gas.
There is no configuration of these contracts in which reopening the bridge is safe.
What actions have been taken to contain the situation
The relevant attacker addresses have been flagged with SEAL, TRM and Chainalysis. We have informed major exchanges and they have suspended SAND deposits and withdrawals from the affected chains. The Sandbox has reached out to the attacker regarding a whitehat return.
The Sandbox continues to coordinate with exchanges, blockchain analytics providers, LayerZero and other security partners. The status of the affected bridge remains under review, and no reopening decision has been made.
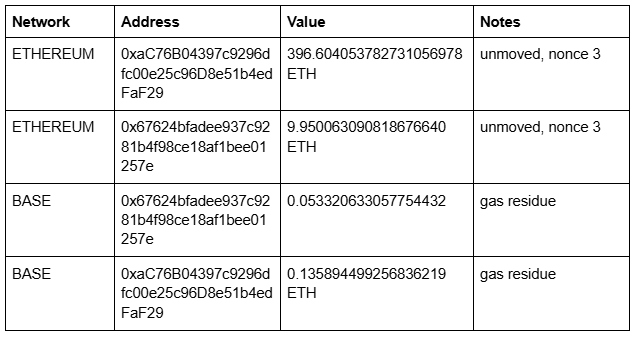
Current status of the attacker’s funds:
What is safe and what isn’t safe to do
What is safe
SAND on Ethereum is unaffected. Its total supply is unchanged at exactly 3,000,000,000 tokens, verified at multiple points before, during and after the incident. No unbacked SAND was created on Ethereum, and nothing about the token contract was altered.
SAND on Polygon is unaffected. Polygon uses a separate bridge that was not part of this integration and was not affected.
Holding, transferring, staking and trading SAND on Ethereum and Polygon remains safe. If your SAND is on either of those networks, nothing has happened to it and you do not need to take any action.
What is not safe
Do not buy SAND on Base or BNB Smart Chain until further notice. A substantial amount of SAND minted on those networks during the incident was not backed by a corresponding deposit on Ethereum. There are more than 339 trillion unbacked SAND (against a real supply of 3 billion), and they cannot be moved to any other network. Whatever price you see quoted for them is not a real price.
Do not send SAND to the Base or BNB Smart Chain bridge contracts. The bridge is permanently closed at contract level on all three networks. Tokens sent to it will be destroyed and nothing will be released in return.
Do not expect the Base or BNB Smart Chain bridge to reopen. Those contracts cannot be repaired because they cannot be upgraded. Bridging to those networks may resume only through newly deployed contracts at new addresses. Any such addresses will be announced through official channels.
Do not trust anyone who contacts you offering to recover, swap or unlock your SAND tokens. Animoca Brands and The Sandbox will never directly message you first offering to recover, swap or unlock your tokens, and no recovery requires you to connect a wallet, sign a message or send funds anywhere. Any such offer is a scam. Compensation for affected holders will be based on balances already recorded on-chain and will be announced through our official channels only.
What is the plan for SAND on Base and BNB Smart Chain going forward
The contracts deployed on Base and BNB Smart Chain are permanently retired, and will not be reopened. Bridging to those networks will be enabled again in the future, but only on newly deployed contracts at new addresses.
Why the existing contracts cannot be reused
- The contracts are not upgradeable. There is no proxy, so the function the attacker used is fixed in the deployed bytecode and cannot be removed, disabled or patched. Anything we deploy to fix this has to be a new contract.
- Control over the bridge configuration cannot be durably held. The design that allowed the attack also means the configuration role can be taken again by anyone willing to pay the gas, however many times it is reclaimed. Reclaiming it would create the appearance of control rather than actual control, which is why we have not done so and why reopening these contracts would be unsafe in any configuration.
What is the current status of the unbacked tokens
The unbacked SAND tokens on Base and BNB Smart Chain are stranded. First, they cannot be bridged to any other chain because the bridge route is set to zero. Second, the send function has been disabled and the vault the unbacked SAND tokens could once be redeemed against is closed. Third, no additional unbacked SAND tokens can be minted.
What we are working towards
The replacement architecture removes the root cause rather than mitigating it. The token and the bridge application will be separate contracts, so that no contract holding a general-purpose call function is also a privileged participant in the bridge. That is the specific combination that made this attack possible, and separating them makes it structurally impossible rather than merely guarded against.
Compensation Plan
Every wallet that held legitimately bridged SAND on Base or BNB Smart Chain immediately prior to the incident will be compensated 1:1 in SAND on Ethereum. Entitlements are determined from balances recorded on-chain immediately before the first unauthorised mint, at Base block 50,283,176 and BSC block 117,321,965. This snapshot is independent of user action, and nothing a holder has done since the exploit affects their entitlement to compensation. The final eligibility criteria will be set out in the claim documentation.
All compensation will be funded from The Sandbox treasury. No new SAND will be minted and the total supply of 3,000,000,000 tokens remains unchanged.
Two centralised exchanges account for over 72% of the affected balance. We are already in direct contact with both and the compensation process is underway, so that their users will be made whole directly through the exchange rather than needing to claim individually.
For all other affected holders, we will publish a claim process for them to receive the equivalent amount of SAND on Ethereum. The claim process will open within the next two weeks and will remain open for two weeks thereafter. The full entitlement list will be published as an X article and a blog post on The Sandbox official website alongside the claim information, enabling users to verify their own balance before claiming compensation. Claiming requires only a transaction from the wallet that held the SAND at the time of the snapshot. Making a claim does not require approving a token, signing an off-chain message, or sending anything anywhere.
Users who do not claim compensation on Ethereum within the next few weeks do not lose their entitlement: the same claim amount will be made available to them on Base and BNB Smart Chain after the replacement contracts have been deployed at their new addresses. We will announce the new addresses for the replacement contracts and the claim details as soon as they are live.
Latest Articles


Copyright © 2012-2026 The Sandbox. All Rights Reserved

Subsidiary of

